
Launch Security Gate
AppDefender, CodeDefender, KeysDefender, and CryptoEngine run natively. Root, jailbreak, emulator, debugger, hooking, overlay. Offline policy is mandatory.
View moreAbout us
Your partner for banks, UPI apps, and fintechs that cannot treat an access token as a security control.
Product suite
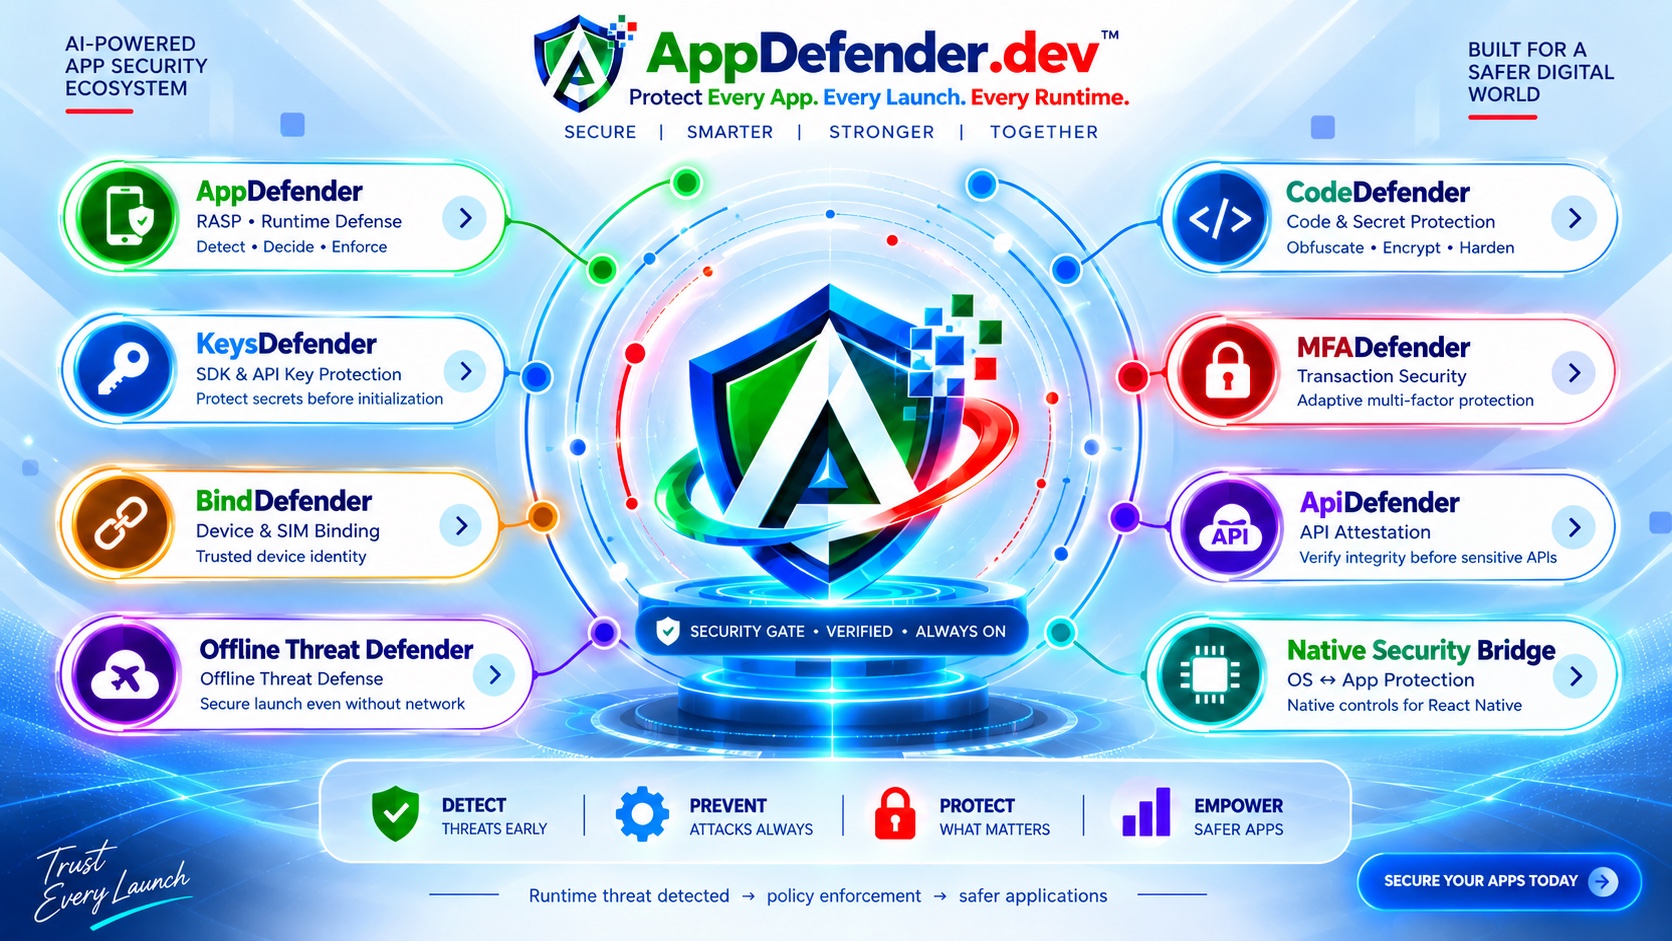
AppDefender Cyber Security Private Limited builds a white-label platform Clients put into React Native, Android, and iOS apps.
Super Admin grants isolated Client Admin. Sandbox and Production stay apart. Production uses Maker–Checker — two makers, two checkers, no self-approval. Built for BFSI and UPI programs, including lending and payment apps that need device binding and transaction binding before money moves.
Why AppDefender.dev exists
Mobile banking, UPI, and lending apps are where customers move money. They are also where overlay, hooking, and cloned devices show up first. An access token does not prove the handset is clean.
AppDefender.dev puts a native Launch Security Gate in front of those apps. Detect on the device. Decide in isolated policy. Enforce ALLOW, RESTRICT, or BLOCK before the Client UI. Offline Threat Handling stays inside that gate.
AppDefender, CodeDefender, KeysDefender, and CryptoEngine run natively. Root, jailbreak, emulator, debugger, hooking, overlay. Offline policy is mandatory.
View moreLogin plus token is never enough. ATS Lite on routine APIs. ATS Full and transaction binding on payments. MITM and token-in-body are rejected.
View moreValues
Clients and their users sit at the center of every launch-gate decision.
Raise the catalog and the console every quarter, not the slogan.
New hooking and overlay families go on the catalog. They do not wait for a rebrand.
Say what the product does. Show credentials once. Never mix environments.
Detect on device. Decide in policy. Enforce before UI. Finish the path.
Sandbox first. Production when Super Admin unlocks it.
Footprint
RASP sensors, catalog, and QA lab.
BFSI and UPI product programs.
Client onboarding and solution engineering.
Banking, UPI, PPI, NBFC lending, insurance.
Industries
Retail and corporate mobile banking with launch-gate RASP.
Lending, PPI, and UPI Client apps with ATS Full on payments.
Policy and claims apps with isolated Sandbox and Production.
Lending programs: Super Admin grants, four seats, isolated catalogs.
App services catalog: Finance appsE-commerce appsHealthcare appsEducation appsTravel appsBanking appsUPI appsBBPS apps
Compliance
Tenant isolation, shown-once credentials, and audit of who enabled Sandbox or Production.
Control mapping for mobile payment apps: device integrity, session binding, and dual control.
Launch-gate RASP and Maker–Checker as evidence packs for operator reviews.
Device integrity, malware signals, and ATS Full transaction binding on payment APIs.
BindDefender and MFADefender keep a session on the enrolled handset and SIM.
Maker–Checker on production policy, Super Admin grants, isolated Client catalogs.
Same 44/23 rule catalog and environment split for PPI and payment-app Clients.
Pinning, key protection, and production dual control as a schedule — not a slide.